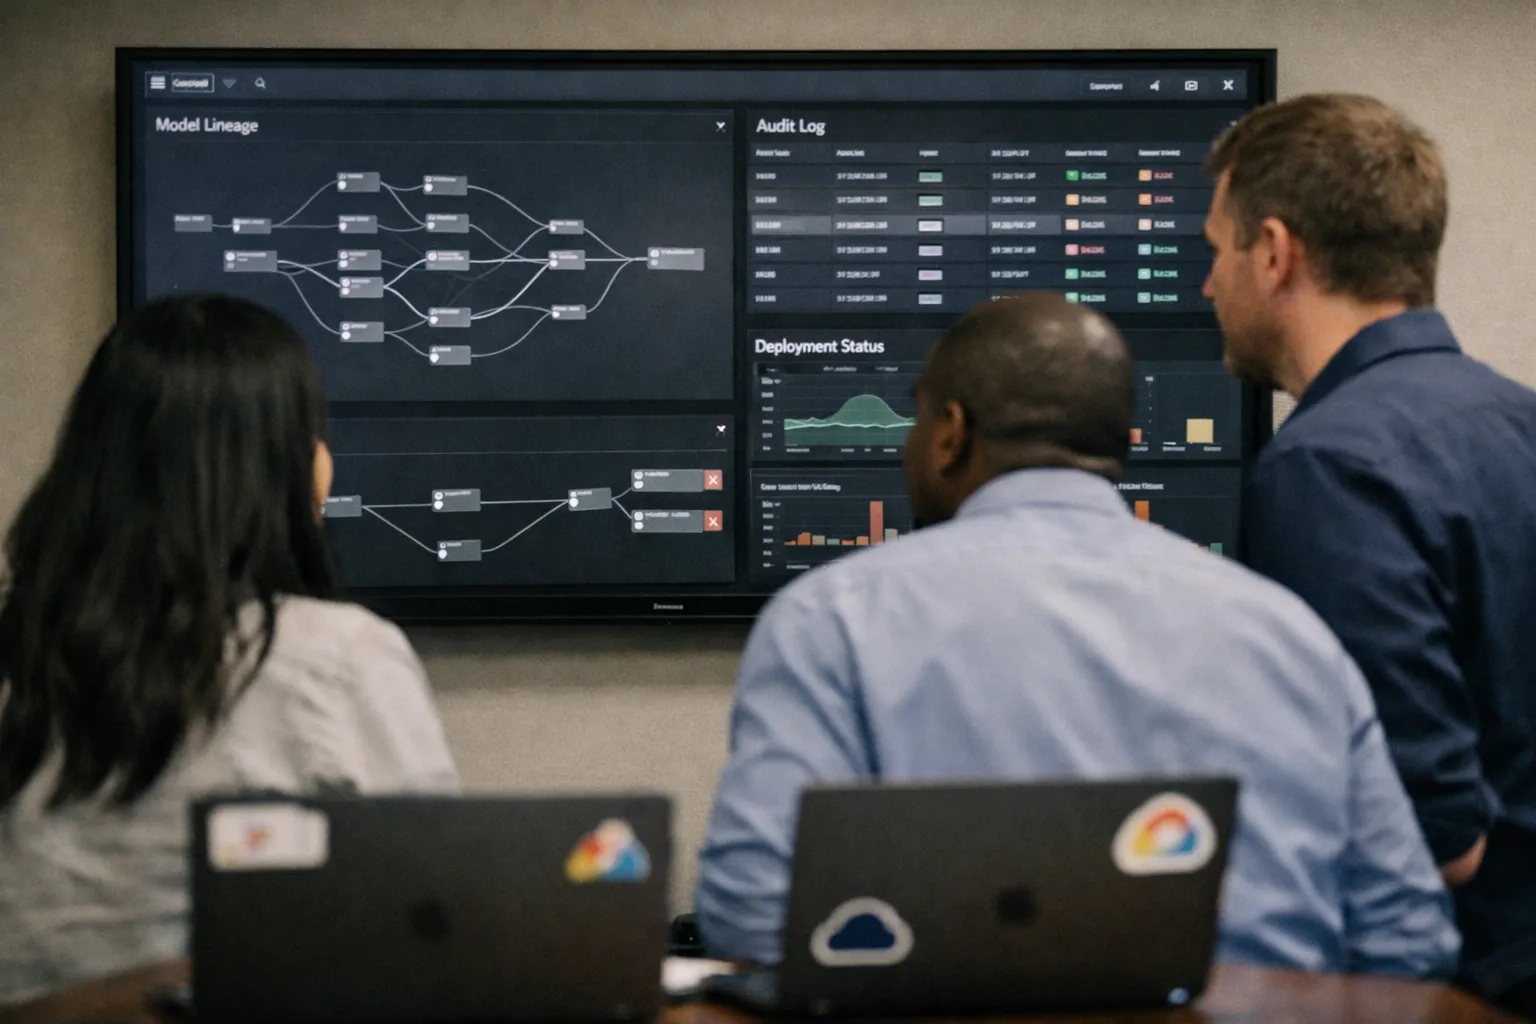
November 2026 — A fresh wave of regulatory pressure in Europe is accelerating changes in enterprise software: vendors are embedding model‑governance controls, auditability, and integration hooks directly into products used for ERP, CRM, search and knowledge management. The shift is reshaping implementation priorities, adding integration work for IT teams, and creating a new calculus for ROI on AI‑augmented enterprise solutions.
Why enforcement is changing vendor roadmaps
Over the past year regulators in the EU and several national authorities have moved from drafting guidance to active enforcement around AI systems deemed high risk. That change has encouraged enterprise‑software vendors to incorporate capabilities that meet compliance needs rather than leaving customers to bolt them on.
Enterprise buyers report the practical results: more product features for model provenance, configurable human‑in‑the‑loop gates, built‑in audit logs, model versioning APIs and standardized documentation such as model cards. These features are intended to make implementation projects predictable from both a technical and compliance perspective while supporting enterprise expectations around scalability and integration.
Feature priorities for enterprise customers
- Provenance and lineage: End‑to‑end tracing of inputs, model versions, and outputs so teams can reconstruct decisions during audits.
- Configurable governance controls: Policy engines that let administrators enforce thresholds, approval flows and human oversight for high‑risk transactions.
- Audit and retention: Tamper‑resistant logs and retention policies compatible with legal hold and eDiscovery processes.
- Integration hooks: API endpoints, webhooks and SDKs that allow model governance to plug into existing identity, SIEM and change‑management platforms.
- Scalability and performance controls: Multi‑tenant isolation, autoscaling policies and resource quotas to ensure governed models perform at enterprise scale.
Implementation becomes a compliance program as much as a technical project
For IT and implementation teams, the change means projects that previously focused on data mapping and user workflows now also require governance design, legal sign‑offs and security integrations. Implementation partners say typical deployments now include an additional governance sprint to map which AI components are high‑risk, define human‑in‑the‑loop thresholds, and integrate model logs into the central audit store.
That added phase affects timelines and budgets. Project managers note a 10–25% uplift in integration time for mid‑sized deployments; for large, regulated organizations that number can be higher. However, vendors contend that the built‑in governance reduces long‑term customization costs and risk, improving net ROI over the lifecycle of the solution.
Integration pain points
- Data residency and telemetry: Enterprises must reconcile model telemetry with data‑residency constraints and existing monitoring solutions, often requiring middleware or secure proxies.
- Identity and access: Governance needs to tie into existing IAM/SSO systems to enforce role‑based controls and approvals, creating additional integration work.
- Versioning across pipelines: Coordinating model versions across CI/CD pipelines, feature stores, and deployment environments remains a common challenge for scale.
How vendors are positioning governance as ROI‑positive
Vendors selling enterprise solutions are framing the new governance features as ROI enablers rather than compliance taxes. Their arguments include:
- Faster procurement and deployment by reducing customers' need for bespoke compliance adapters.
- Lower audit and liability risk by providing built‑in trails, which shrinks legal review cycles and insurance costs.
- Improved operational continuity: policies and human‑in‑the‑loop workflows can prevent model drift from causing systemic issues at scale.
Enterprise purchasers say the value depends on how closely the vendor features match their compliance requirements and how cleanly they integrate into existing monitoring and IAM stacks. When alignment is strong, procurement cycles shorten and projected ROI improves; when integration is manual, ROI is delayed.
What CIOs and SREs are asking vendors for
From conversations with implementation teams and systems engineers, the top vendor requests are:
- Standardized model‑governance APIs that work across cloud providers and private deployments to minimize vendor lock‑in.
- Configurable scalability controls to run governed inference at the throughput required by core business processes.
- Clear SLAs for auditability features (e.g., log retention guarantees, export formats and tamper evidence).
- Prebuilt integrations to SIEM, GRC and backup platforms so governance artifacts are part of existing observability and continuity plans.
Market implications and next steps
In the short term, organizations should expect implementation bids that explicitly list governance deliverables, integration tasks, and compliance validation steps. Procurement teams need to update RFP templates to request model‑governance compliance artifacts and test plans. System architects should add a governance sprint to project timelines to map controls and integration touchpoints.
Over the medium term, these governance primitives could settle into vendor ecosystems as standard features, reducing the integration burden and improving economies of scale for governance. That would permit enterprise buyers to focus on use‑case optimization rather than compliance mechanics — a shift that would materially improve ROI for AI‑enabled enterprise solutions.
Bottom line
Regulatory pressure in late 2026 is forcing a structural change: model governance is moving from the margins into the core of enterprise software. For CIOs and SREs, the immediate challenge is implementation and integration — ensuring governance scales and integrates with identity, observability and audit systems. For vendors, the opportunity is to turn governance into an integration‑friendly feature set that delivers measurable ROI rather than an expensive compliance bolt‑on.