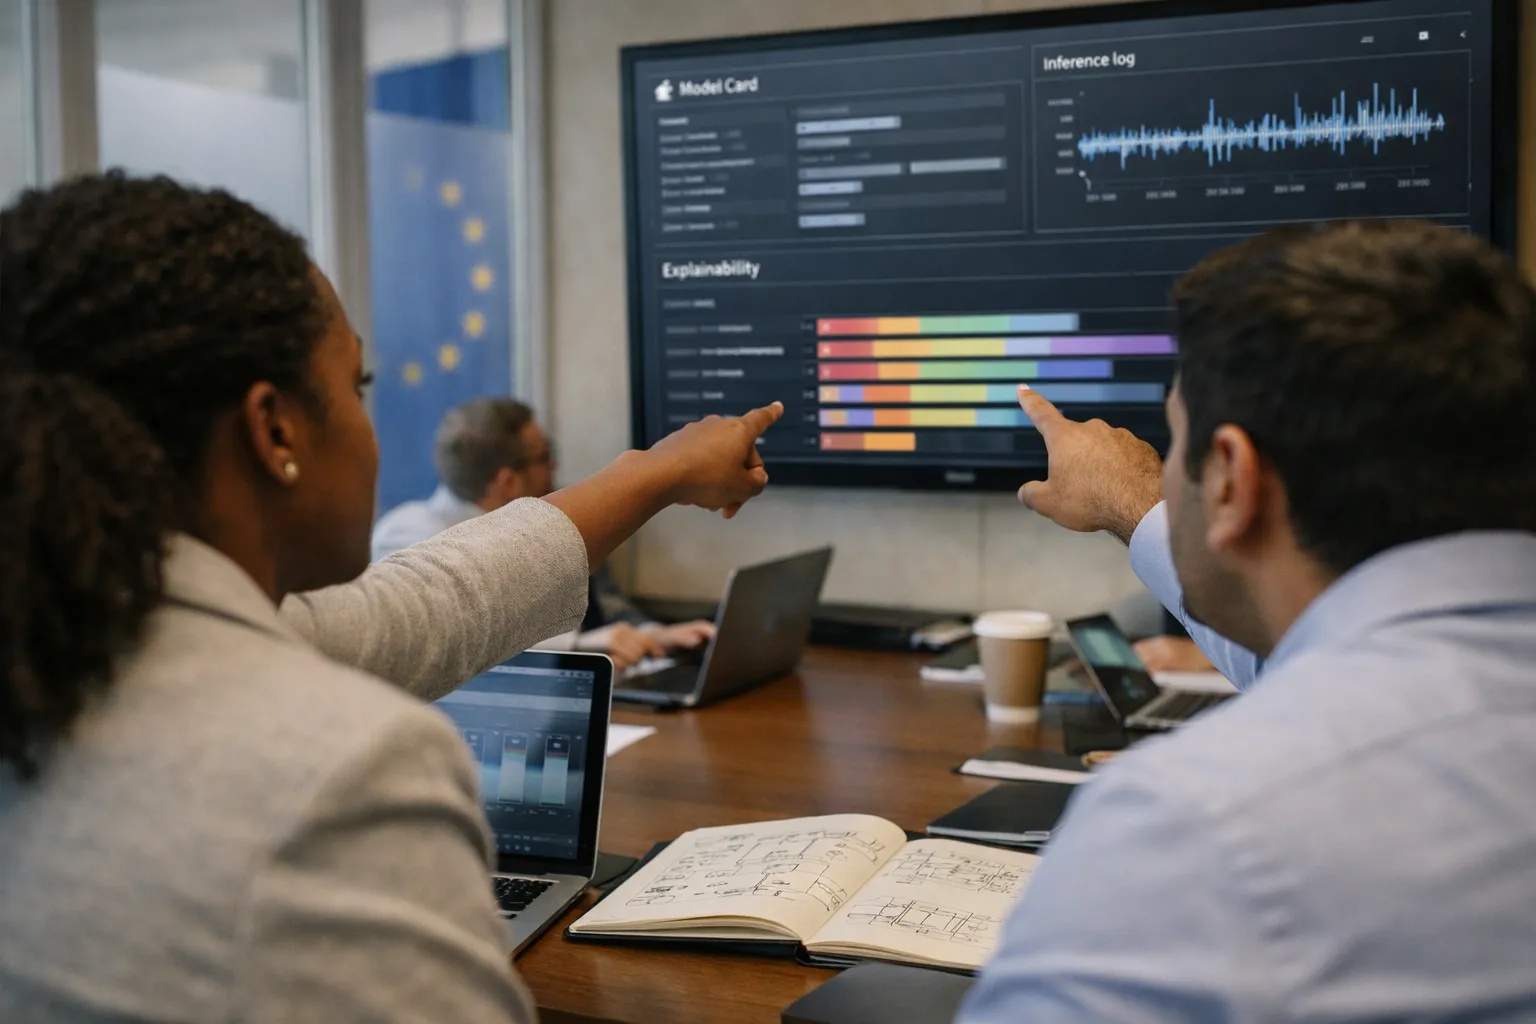
The EU AI Act is accelerating a concrete shift in enterprise software design: vendors and platform teams are increasingly embedding model documentation, runtime audit trails and explainability hooks directly into enterprise solutions. The change is less about novel research and more about operationalizing compliance controls inside existing MLOps and application stacks — an effort that touches integration, scalability and ROI calculations across large organizations.
Why this is news now
Regulatory attention around high‑risk AI systems has crystallized implementation requirements that used to be optional or ad‑hoc. The AI Act’s baseline obligations — risk management systems, technical documentation, record‑keeping (including logs of model inputs and decisions), human oversight, transparency and post‑deployment monitoring — map directly onto engineering and operational tasks. For enterprise software providers and their customers, meeting those obligations means adding new technical capabilities to product roadmaps and implementation plans.
From paper policies to built‑in controls
Historically, enterprises met compliance by adding external audits, manual documentation and periodic reviews. That model breaks down at scale. Two practical patterns have emerged:
- Built‑in documentation: model cards and datasheets become first‑class artifacts produced automatically during model training and registered alongside artifacts in model registries.
- Runtime observability: systematic logging of inputs, outputs, confidence metrics and drift indicators at inference time to support post‑hoc audits and incident investigations.
Both patterns are being implemented inside enterprise solutions — not as aftermarket bolt‑ons — so that audit artifacts are generated as part of routine CI/CD and deployment pipelines.
Integration and implementation challenges
Embedding these features into existing enterprise stacks raises technical and programmatic trade‑offs that CIOs and architects must weigh.
1. Integration complexity
- Model registries, feature stores and observability platforms must exchange metadata consistently. That often requires upgrading APIs, adding schema governance and deploying connectors between systems.
- Enterprises with heterogeneous tech stacks (on‑premise infrastructure, multiple clouds, third‑party SaaS) face tougher integration scenarios; mapping a common compliance event model across silos is non‑trivial.
2. Scalability and performance
Runtime logging and explainability at inference time add compute, storage and latency overhead. Design choices include sampling (only retain a subset of inferences), asynchronous logging, or edge‑level aggregation to balance compliance fidelity with service level objectives.
3. Data governance and privacy
Record‑keeping obligations can conflict with data minimization and privacy rules. Enterprises must define what to log (e.g., hashes of inputs vs raw inputs), retention periods and access controls so that auditability does not create new compliance risks.
4. Implementation velocity vs ROI
Embedding compliance features has upfront costs: engineering effort, increased infrastructure spend, and slower release cycles while controls are validated. The ROI argument rests on reduced regulatory risk, faster audits, fewer costly incidents, and potential competitive advantage. Quantifying that ROI requires mapping expected cost reductions (audit time, remediations) against implementation and ongoing operational costs.
Practical patterns vendors and customers are adopting
Enterprises that are moving fastest adopt a few repeatable patterns:
- Artifact‑first pipelines: Produce model cards, training data lineage and evaluation reports automatically and store them in searchable registries so documentation is discoverable during audits.
- Event‑driven observability: Emit structured inference events into an event bus or observability layer that supports retention, replay and query for investigations.
- Explainability at scale: Precompute feature attributions for common input archetypes and use lightweight local explainers for real‑time requests to reduce latency costs.
- Policy templates and guardrails: Standardized, declarative policy definitions (e.g., what triggers human review) integrated into deployment pipelines make implementation repeatable across teams.
How this affects vendor selection and product roadmaps
Enterprise buyers are updating evaluation criteria. Where architecture RFPs once prioritized throughput and cost per inference, they now include questions about built‑in documentation exports, tamper‑evident logs, role‑based access for audit artifacts, and native explainability SDKs. That changes vendor roadmaps: platform vendors must provide turnkey controls or risk losing deals to incumbents that can demonstrate operational compliance capabilities.
For ISVs and platform teams, this is also an opportunity: integrating compliance features into core product offerings can become a differentiator, particularly for regulated sectors such as finance, healthcare and public services. However, product teams must be explicit about the tradeoffs — e.g., whether explainability is provided synchronously, asynchronously, or as a sampled background process — and how those choices affect scalability and total cost of ownership.
Checklist for enterprise architects
To translate regulatory requirements into engineering work, architects should consider this minimum checklist during implementation:
- Define the scope of “high‑risk” models and map them to required documentation and monitoring frequency.
- Standardize a metadata schema for model cards, dataset lineage and evaluation metrics and enforce it via CI gates.
- Instrument inference pipelines to emit structured events that include model version, input hashes, output, confidence scores and decision metadata.
- Decide storage and retention strategies for logs that balance auditability, privacy and cost.
- Plan for explainability tradeoffs — precomputation, sampling or lightweight on‑path explainers — and test for latency impact under load.
- Estimate incremental costs and run a basic ROI model that contrasts compliance costs with avoided fines, remediation expenses and operational savings.
Bottom line
The EU AI Act and similar regulatory signals are turning what was previously optional documentation and observability work into implementation requirements. For enterprise software teams, the shift means embedding compliance capabilities into the fabric of enterprise solutions so they scale with usage and integrate cleanly across existing systems. The technical challenges — integration complexity, scalability penalties and privacy tradeoffs — are surmountable, but require early architecture decisions and explicit ROI modeling to justify the investment.