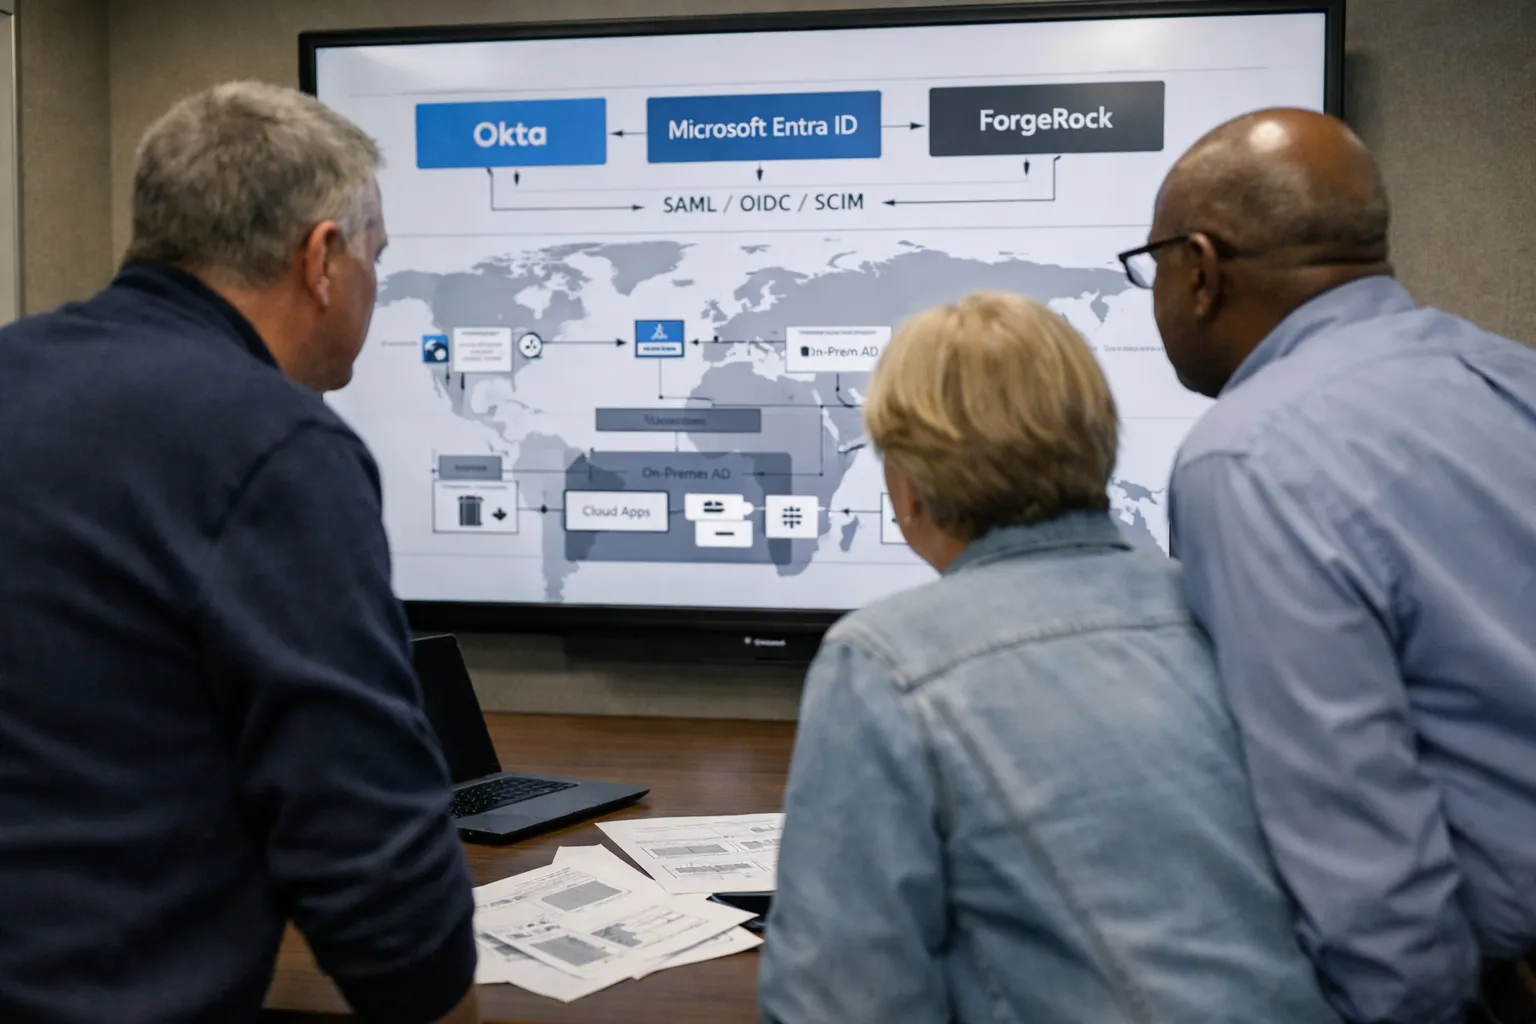
Enterprises evaluating identity platforms in August 2026 face a landscape shaped by three clear forces: passwordless adoption and passkeys, AI-driven fraud and identity proofing, and regulatory pressure for data locality and observability. The core choice remains the same as in 2024–25: use a cloud-native vendor-neutral identity plane, rely on the cloud platform’s native identity service, or deploy a hybrid/on‑prem solution for maximum control. This update compares Okta, Microsoft Entra ID and ForgeRock against the criteria that matter now—scalability, integration breadth, security and compliance, implementation complexity and ROI—and adds new guidance for AI, passkeys and identity operationalization.
Comparison criteria — what matters in 2026
Decision-makers should evaluate vendors across the following updated criteria:
- Scalability: ability to handle spikes, global latency, and multi‑tenant tenancy while meeting data‑sovereignty controls.
- Integration breadth: SSO, provisioning (SCIM), device posture, IAM-to-cloud-provider control planes and identity-as-code toolchains.
- Security & fraud prevention: adaptive auth, passkey/FIDO2 support, AI-based risk signals, credential-less flows and account takeover mitigation.
- Compliance & data locality: ability to isolate identity data by region and provide audit-ready telemetry for regulators.
- Operational model: SaaS vs hybrid vs on-prem, required ops headcount, and vendor-managed capabilities (SRE/SOC for identity).
- Cost & ROI: licensing, hidden integration costs, ops, and business outcomes (reduced friction, faster partner onboarding, fraud reduction).
Why these three?
Okta, Microsoft Entra ID and ForgeRock continue to represent distinct strategic approaches:
- Okta — cloud-first vendor-neutral identity platform optimized for diverse enterprise stacks and third-party SaaS.
- Microsoft Entra ID — the native identity plane for Microsoft clouds and Windows-centric enterprises, now central to many organizations’ zero‑trust deployments.
- ForgeRock — a hybrid/on-prem identity platform focused on customer identity, data residency controls and extensive customization.
Updated high-level summary (Aug 2026)
- Okta: Best for multi-cloud enterprises that need rapid SaaS SSO, extensive third‑party connectors and mature passkey/passwordless support with an API-first approach.
- Microsoft Entra ID: Best when Microsoft 365, Azure, Windows and Intune are central; excels at device-tied conditional access and licensing economies for Microsoft-heavy shops.
- ForgeRock: Best where in-country residency, deep customization of customer journeys, or complex B2C/B2B orchestration are non-negotiable.
Scalability in 2026 — what’s changed
Scalability still means handling authentication throughput and administrative scale, but the bar has risen: passkey deployments and real‑time fraud checks add sustained traffic, and AI-based risk engines increase telemetry volumes.
- Okta: Continues to operate as a global multi‑tenant SaaS with regional data hosting options for selected markets. Pros: near-instant elasticity for authentication peaks and built-in rate control; many customers report simpler passkey rollouts compared with bespoke on‑prem platforms. Cons: true in-region custody for regulated workloads often requires hybrid patterns or contractual data‑restriction addenda.
- Entra ID: Scales natively inside Azure and benefits from Microsoft's global backbone. Pros: native hybrid identity tools (Azure AD Connect / hybrid join patterns) and deep integration with Microsoft endpoint telemetry reduce bottlenecks for Microsoft-centric fleets. Cons: when an enterprise's workloads span multiple clouds with different identity requirements, additional bridging layers are required.
- ForgeRock: Designed for distributed or on‑prem clusters; you can architect strong regional isolation and keep authentication fully in-country. Pros: low-latency in-region auth and explicit control of replication. Cons: requires more ops investment (capacity planning, monitoring, SRE) relative to the SaaS options.
Integration and interoperability — new 2026 considerations
Key integration needs in 2026: passkeys/FIDO2 for workforce and customers, verifiable credentials for regulated use cases, CIEM/CSPM interoperability, and identity-as-code workflows.
- Protocols: All three support SAML, OIDC, OAuth2, SCIM and LDAP. FIDO2/passkey support is now table stakes for workforce SSO; all vendors provide passkey tooling, but implementation complexity varies for B2C large-scale deployments.
- Enterprise systems:
- Okta: excels at thousands of ready-made connectors for SaaS, developer SDKs and an ecosystem that supports identity-as-code patterns (APIs and Terraform providers are common in large Okta deployments).
- Entra ID: offers deep native hooks into Windows sign-in, Intune device posture, Defender signals and Microsoft cloud services—reducing friction when endpoints are Microsoft-managed.
- ForgeRock: provides stronger integration paths for legacy LDAP directories, mainframe adapters and customizable orchestration for complex customer identity journeys (progressive profiling, multi-tiered consent).
- Multi-cloud pattern: For heterogeneous SaaS-heavy estates, Okta reduces friction. When identity must be a native extension of Azure tenants, Entra ID minimizes engineering overhead. For regulated or legacy environments that require in‑country identity flows, ForgeRock remains the practical choice.
Security, governance and AI-driven fraud prevention
Between 2024 and 2026, two clear shifts affected vendor capabilities: mainstream passkey adoption and the use of AI/ML for fraud detection and identity proofing. Vendors now differentiate on the fidelity of their risk signals and how they integrate third‑party telemetry.
- Okta: Strong adaptive MFA and device insight via integrations; broad passkey tooling and developer SDKs. Okta’s identity threat detection capabilities emphasize cross-app telemetry and lifecycle monitoring; many customers use Okta in concert with third‑party fraud vendors for high-value customer transactions.
- Entra ID: Conditional Access remains a strength—device compliance, Defender risk signals and contextual policies combine for robust access decisions in Microsoft-centric estates. Entra’s integration with Microsoft Defender and Intune makes behavior and device telemetry tightly coupled to policy enforcement.
- ForgeRock: Emphasizes privacy, consent and fine‑grained authorization. For customer identity, ForgeRock deployments commonly embed specialized fraud models and bespoke identity proofing workflows that are harder to achieve with off-the-shelf SaaS providers.
Regulatory note: data locality and observability requirements (EU, APAC) have matured—expect auditors to ask not just where identity data is hosted but how AI models used for risk scoring are logged and explainable.
Implementation effort, migration and operational practices
Implementation effort remains a top ROI driver. New in 2026: the operational model often includes identity SRE, runbooks for passkey lifecycle, and model‑validation for AI-based fraud engines.
- Okta: Fastest time-to-value for SaaS SSO and developer integrations. Typical outcome: SSO for dozens of SaaS apps in weeks and staged passkey rollout across workforce in months. Use identity-as-code templates and Terraform providers to automate configuration drift.
- Entra ID: Quick when the estate is Microsoft-heavy. Hybrid join and device-based conditional access patterns are well documented. Migration complexity increases when connecting non-Microsoft on-prem systems or multi-cloud workloads.
- ForgeRock: Longer planning and implementation cycles for hybrid/on‑prem. The trade-off is control: bespoke consent, regional replication and complex B2C orchestration that vendors’ SaaS offerings may not accommodate without extensive customization.
Cost structure and ROI — updated dynamics
Vendor pricing models evolved: more vendors offer feature bundles, regional-hosting premiums, and usage-based pricing for high-volume customer authentication. ROI calculation now must include fraud reduction, passkey-driven reduction in password resets, and identity telemetry costs (storage and SIEM ingestion).
- Okta: Per-user and per-feature licensing remains common; expect additional fees for enterprise identity governance, customer identity tiers and regional hosting. ROI is fastest when you quantify helpdesk savings and app onboarding time.
- Entra ID: Licensing continues to be attractive inside Microsoft Enterprise Agreements; companies standardizing on Microsoft services often see consolidated billing and easier procurement. Evaluate costs for premium conditional access features and cross-cloud connectors.
- ForgeRock: Higher up-front TCO for software, infrastructure and ops, but justified when regulatory or customer experience requirements cannot be met by SaaS vendors. Consider multi-year TCO and benefits from in-country hosting and bespoke fraud mitigation.
Side-by-side snapshot (practical points)
- Passkeys/Passwordless: All three support FIDO2/passkeys; Okta and Entra ID streamline workforce rollouts; ForgeRock is commonly chosen for large-scale customer passkey programs needing bespoke UX.
- Data residency: ForgeRock (on‑prem/hybrid) gives the most precise control; vendors offer regional hosting for enterprise tiers—verify contractual terms and auditability.
- AI risk scoring: Okta and Entra ID provide built-in risk engines and vendor telemetry; ForgeRock customers more often integrate third‑party fraud engines or build custom ML pipelines.
- Operational demand: Okta/Entra ID require less ops headcount; ForgeRock requires experienced ops/SRE for stateful clusters.
Choose this if… (updated recommendations)
- Choose Okta if you run a heterogeneous, SaaS-heavy estate, value fast time-to-value, and want robust developer tooling and passkey support with vendor-hosted regional options.
- Choose Microsoft Entra ID if your identity plane must be tightly integrated with Windows, Microsoft 365, Intune and Azure, and you want consolidated licensing and device-tied conditional access.
- Choose ForgeRock if you require strict in-country identity processing, complex customer journeys (B2C/B2B), or bespoke identity orchestration that off-the-shelf SaaS cannot deliver.
Decision checklist for technical buyers (2026 edition)
- Inventory apps, identity stores and user populations (employees, partners, customers) and measure peak auth rates including passkey and fraud checks.
- Decide control vs speed: do you need strict local custody and custom ML, or faster SaaS delivery?
- Platform alignment: are you Microsoft-centralized or multi-cloud heterogeneous?
- Operational readiness: can your team run identity SRE and validate AI risk models?
- Compliance: confirm contractual data residency, model explainability and audit logs for identity risk scoring.
- ROI horizon: include fraud reduction, helpdesk savings, conversion uplift from better customer journeys and cost of telemetry ingestion.
Implementation tips — practical and current
- Run a two-track pilot: workforce passkeys + a small customer B2C flow. Validate reset reductions, conversion rates and fraud signals over 90 days.
- Adopt identity-as-code: use Terraform/CloudFormation providers and CI pipelines to manage policy drift and enable repeatable multi-region deployments.
- Instrument telemetry before go-live: capture auth, decision context and AI model inputs so you can measure ROI and satisfy auditors.
- Staged passkey rollout: start with IT and high-risk groups, then expand. Provide fallback and clear UX for recovery to reduce lockout risk.
- Plan for model governance: keep logs and an audit trail for any AI/ML risk signals used in access decisions—regulators increasingly ask for this evidence.
Conclusion
As of August 2026, Okta, Microsoft Entra ID and ForgeRock remain mature options for hybrid-cloud IAM but the buying calculus has evolved. Passwordless and passkeys are mainstream; AI-driven fraud detection and model governance matter in procurement; and data residency plus auditability often make the difference between a SaaS choice and a hybrid/on‑prem solution. Use the updated checklist above to match technical capabilities, operational readiness and regulatory constraints to the vendor profile that best fits your enterprise priorities.
FAQ
Is passkey adoption now a requirement for enterprise IAM?
No—passkeys are not mandatory, but they are increasingly required to meet security and user-experience goals. By 2026 most enterprise-grade IAM platforms provide mature passkey tooling for workforce and customer flows. Implementing passkeys reduces password-reset costs and improves phishing resilience, but plan for recovery options and phased rollouts.
Can I use Entra ID as my identity plane if I run multi-cloud workloads?
Yes, Entra ID can act as an identity plane for multi-cloud workloads, but expect additional integration work for non-Microsoft clouds and tooling. If your estate is predominantly Microsoft, Entra ID reduces friction; if you depend heavily on third‑party SaaS and heterogeneous identity sources, a vendor-neutral plane like Okta may reduce long-term integration overhead.
When is ForgeRock the right choice over a SaaS provider?
Choose ForgeRock when regulatory requirements demand strict in‑country identity processing, or when you need bespoke customer journey orchestration that off-the-shelf SaaS cannot deliver reliably. The trade-off is higher implementation and operational costs; plan for an SRE and longer project timelines.
How should I account for AI-driven risk engines in procurement?
Require vendors to disclose what telemetry their risk engines use, how models are validated and how decisions are logged. Include SLAs for false positives/negatives where feasible and plan to retain audit logs long enough to satisfy regulators and internal compliance requirements.
What ROI signals should I measure first?
Start with measurable, fast indicators: reduction in password-reset tickets, time-to-onboard new SaaS apps or partners, authentication latency and a baseline fraud rate for customer transactions. These map directly to helpdesk cost savings, developer productivity and revenue protection.