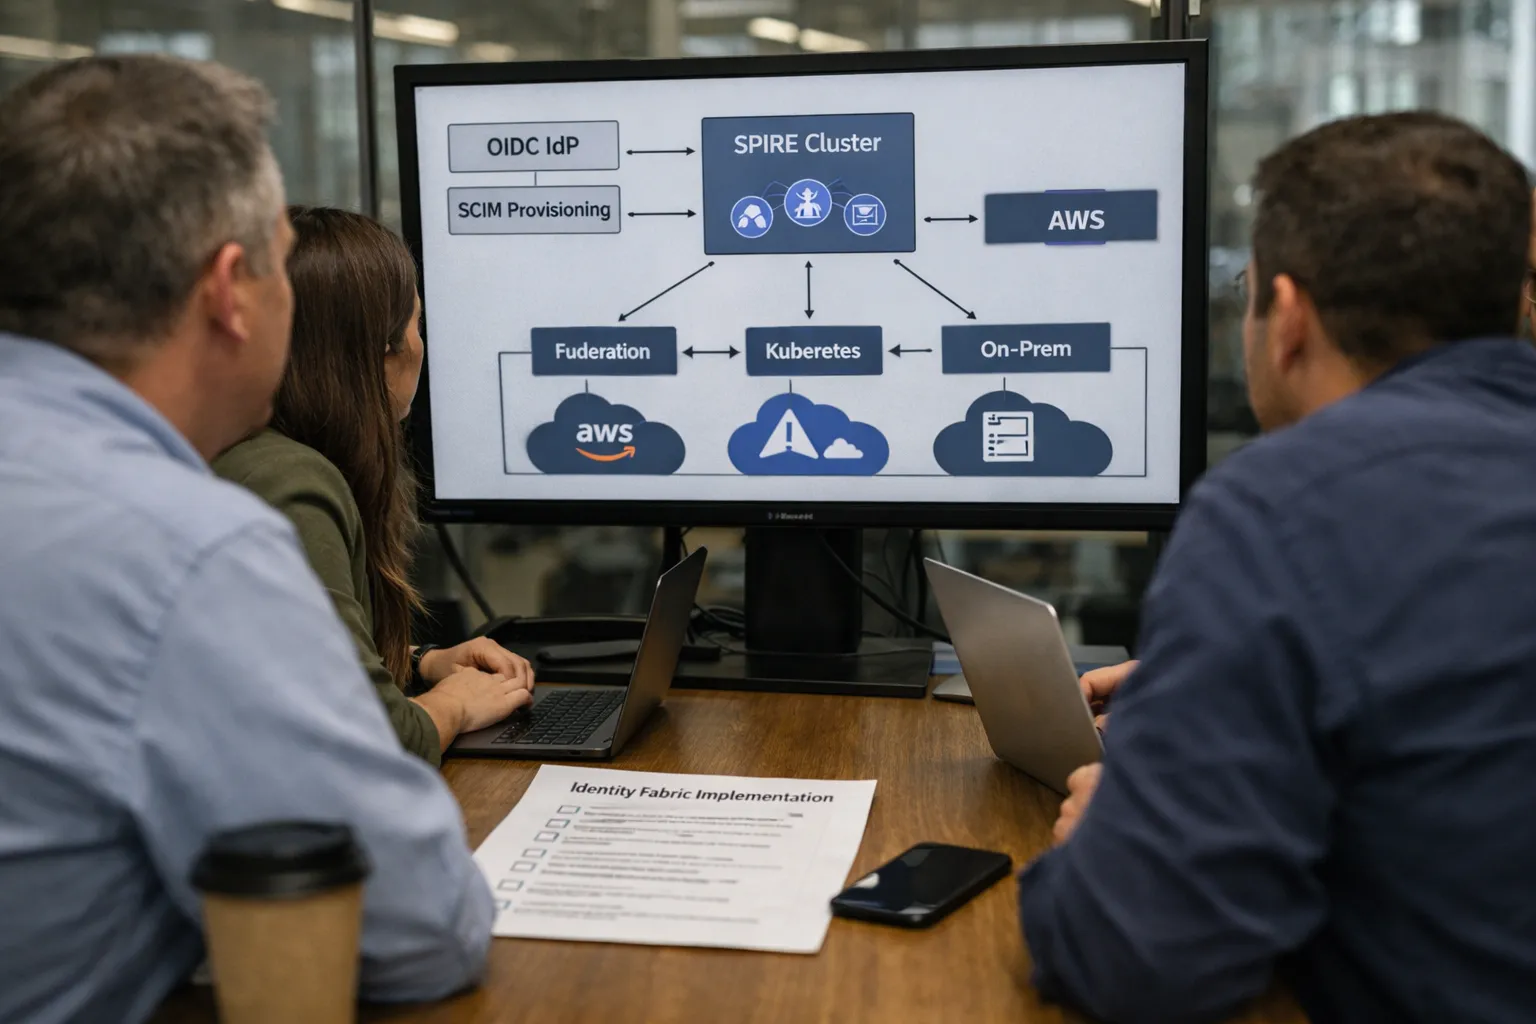
As enterprises adopt multi-cloud, hybrid-cloud and distributed microservices architectures, identity becomes the glue for secure, scalable integration. A modern identity fabric stitches human SSO, automated provisioning and workload identity into a unified model that supports enterprise solutions at scale. This guide walks architects and platform engineers through a practical, vendor-agnostic implementation using OpenID Connect (OIDC) for human authentication, SCIM for user provisioning, and SPIFFE/SPIRE for workload identity and mTLS — delivering integration, scalability and measurable ROI.
Why a cross‑cloud identity fabric matters
Traditional identity setups — siloed SSO portals, bespoke provisioning scripts, and ad‑hoc service certificates — break down under scale. Problems include:
- Inconsistent identity lifecycles across clouds and SaaS apps
- High manual overhead for user onboarding and offboarding
- Service-to-service authentication that is brittle, unmanaged or reliant on long-lived static credentials
- Poor auditability and complex compliance reporting
A well-designed identity fabric addresses these by unifying authentication, provisioning and workload identity. Benefits include improved security posture, faster application onboarding, and operational cost reductions that translate into clear ROI.
Core building blocks (and why they matter)
For enterprise implementations targeting broad integration and scalability, adopt three complementary standards:
- OIDC (OpenID Connect) — modern SSO and delegated identity for humans and service accounts. Works with OAuth 2.1 best practices and supports federated login across identity providers (IdPs) like Okta, Azure AD, AWS IAM Identity Center and Keycloak.
- SCIM 2.0 — standardized user provisioning and lifecycle API that automates create/update/delete operations for users/groups across SaaS and cloud directories.
- SPIFFE/SPIRE — a standards-based workload identity framework that issues short‑lived X.509 SVIDs or JWTs for services, enabling mTLS and mutual authentication across platforms without static secrets.
When to build this vs. buy a commercial identity fabric
Choose build when:
- You need deep control of workload identity across private clouds, Kubernetes clusters and legacy data centers.
- Your compliance requirements include custom audit events or integration with on-prem HSMs.
- You have a platform team capable of operating SPIRE and federation components at scale.
Choose buy (commercial identity platforms or managed SPIFFE offerings) when you want quicker time-to-value, vendor SLAs, and integrations out-of-the-box with major SaaS platforms. In many enterprises a hybrid approach (commercial IdP + open-source workload identity) is optimal.
High-level architecture
Design an architecture with clear trust boundaries and orchestration points:
- Identity Provider Layer: Okta, Azure AD, Google Workspace, AWS IAM Identity Center or Keycloak for OIDC authentication and federation.
- Provisioning Layer: SCIM connectors from IdPs to SaaS apps, cloud directories and HRIS.
- Workload Identity Layer: SPIRE servers per trust domain issuing short-lived SVIDs; sidecars or service mesh (Istio, Linkerd or Consul) enforcing mTLS and policy.
- Control Plane: A central identity orchestration plane for policy, audit logs, and certificate lifecycle orchestration (can be integrated with SIEM/IDAM).
- Observability & Audit: Centralized logs and metrics for provisioning events, token issuance, and SVID rotation.
Step‑by‑step implementation plan
Below is a pragmatic phased approach you can use as a template for 3–9 month implementations depending on scope.
Phase 0 — Assessment (2–4 weeks)
- Inventory: catalog apps, SaaS, cloud accounts, Kubernetes clusters, legacy services, existing IdPs, provisioning processes and current certificate management.
- Use cases: define primary use cases (employee SSO, contractor accounts, CI/CD service identities, inter-cluster mTLS).
- Compliance & risk: map regulatory requirements and audit expectations.
- KPIs for ROI: set measurable targets (onboarding time, mean time to revoke, failed auth incidents, ops hours saved).
Phase 1 — OIDC SSO and Federation (4–8 weeks)
- Select IdP(s): prefer existing enterprise IdP for SSO federation. For multi‑region resilience, set up primary and backup IdPs with SAML/OIDC federation.
- Implement OIDC flows: adopt authorization code with PKCE for public clients and standard code flow for confidential clients. Ensure OAuth 2.1 best practices (refresh token handling, token lifetimes).
- Standardize claims and scopes: define a canonical claims schema (email, sub, tenant, roles) for services to consume.
- Integrate apps: replace legacy SAML where possible with OIDC; for legacy apps keep a SAML-to-OIDC bridge.
Phase 2 — Automated provisioning with SCIM (4–8 weeks)
- Map source of truth: typically HRIS for full-time employees and an identity registry for contractors.
- Implement SCIM endpoints or use an IdP’s built-in connectors to provision users and groups to SaaS apps and cloud directories.
- Define lifecycle rules: onboarding templates, attribute mappings, role-to-group logic, and offboarding flows that immediately disable access on termination.
- Test reconciliation: schedule periodic reconciliation checks and alerts on mismatches.
Phase 3 — Workload identity with SPIFFE/SPIRE (8–12 weeks)
- Establish trust domains: define a trust domain per administrative boundary (e.g., prod, dev, cloud-account).
- Deploy SPIRE servers: deploy SPIRE server cluster per trust domain with HA and storage backend (e.g., etcd or relational DB supported by SPIRE).
- Bootstrap agents: install SPIRE agents in Kubernetes nodes, VMs and containers where services run.
- Integrate with mesh: configure Istio/Linkerd/Consul to validate SVIDs and enforce mTLS between services.
- CI/CD integration: extend pipelines to request ephemeral identities for jobs and ephemeral infrastructure.
Phase 4 — Integration, policy and observability (4–8 weeks)
- Central policy: map RBAC roles across human and workload identities; implement policy-as-code (OPA/Gatekeeper) where appropriate.
- Audit pipelines: forward token issuance, SCIM provisioning events and SVID rotation logs to your SIEM (Splunk/Elastic/Datadog).
- Monitoring: instrument identity services (IdP, SPIRE, SCIM connectors) with SLOs and alerting.
- Operational runbooks: revoke flows, failover plans for IdP or SPIRE outages, emergency access procedures.
Integration patterns and practical tips
- Federation-first approach: keep a single canonical identity source per employee and federate to cloud providers to reduce duplication.
- Progressive rollout: start with non-critical apps and a small cluster to validate SPIRE and mesh enforcement before full production cutover.
- Service account hygiene: replace long-lived keys with short-lived tokens and SVIDs; enforce rotation via SPIRE and automated pipeline workflows.
- Zero trust alignment: use the identity fabric as the foundation of a zero-trust posture — authenticate + authorize for every request, not just network perimeter.
Scalability considerations
To scale the identity fabric:
- Partition trust domains to limit blast radius while preserving cross-domain trust where required.
- Use regional SPIRE clusters with replication for low-latency SVID issuance.
- Cache tokens and certificates short-term at service sidecars but avoid long-lived credentials; enforce short TTLs for stronger security at scale.
- Automate connector lifecycle; use IaC (Terraform/CloudFormation) to provision IdP connectors and SCIM client configurations.
Measuring ROI
Quantify ROI with pre-defined KPIs:
- Onboarding time: measure average time to provision new hires before/after SCIM. Savings often manifest as days reduced to hours.
- Operational hours saved: estimate weekly hours platform and IT ops spend on manual provisioning, certificate rotation and incident recovery.
- Reduction in security incidents: track incidents caused by credential misuse and time-to-revoke; shorter token lifetimes and instant revocation reduce exposure.
- Compliance cost reduction: faster audits and consolidated logs reduce audit preparation time and expense.
Present a 12–24 month TCO comparison including implementation effort, licensing (IdP or managed SPIFFE), and ongoing ops. Include tangible outcomes such as reduced onboarding costs and lower incident remediation time to build a business case.
Migrations and cutover strategies
- Parallel run: run legacy and new systems in parallel and route a percentage of traffic to the new identity fabric.
- Canary provisioning: enable SCIM for a subgroup of users to validate mappings and reconcile differences.
- Emergency rollback: keep rollback steps and pre-authorized emergency access to avoid service lockouts during cutover.
Common pitfalls and how to avoid them
- Underscoping policy: Don't treat workload and human identity as separate projects; align RBAC and attribute models across both.
- Overreliance on a single vendor: Plan for IdP failover and federation to reduce vendor lock-in risk.
- Ignoring observability: Identity systems are high-value attack surfaces — instrument everything from token issuance to provisioning events.
- Poor developer ergonomics: provide SDKs, sample code and libraries that simplify OIDC and SPIFFE usage for app teams to accelerate adoption.
Checklist for a successful implementation
- Inventory completed and use cases prioritized.
- Canonical identity source defined and federated.
- OIDC SSO implemented with standardized claims.
- SCIM provisioning automated for top SaaS applications.
- SPIRE deployed and integrated with service mesh for workload identity.
- Policy, logging, and monitoring integrated into central SIEM.
- Runbooks, rollback plans and SLA agreements in place.
- ROI metrics defined and baseline measurements taken.
Conclusion
Building an enterprise cross‑cloud identity fabric that combines OIDC for authentication, SCIM for provisioning and SPIFFE for workload identity delivers a scalable, integrable foundation for modern enterprise solutions. The implementation requires coordination across security, platform and application teams, but the payoff — improved security posture, faster onboarding, lower operational cost and demonstrable ROI — makes it a strategic investment. Use the phased plan above, measure outcomes, and iterate: identity is a platform, not a one-time project.