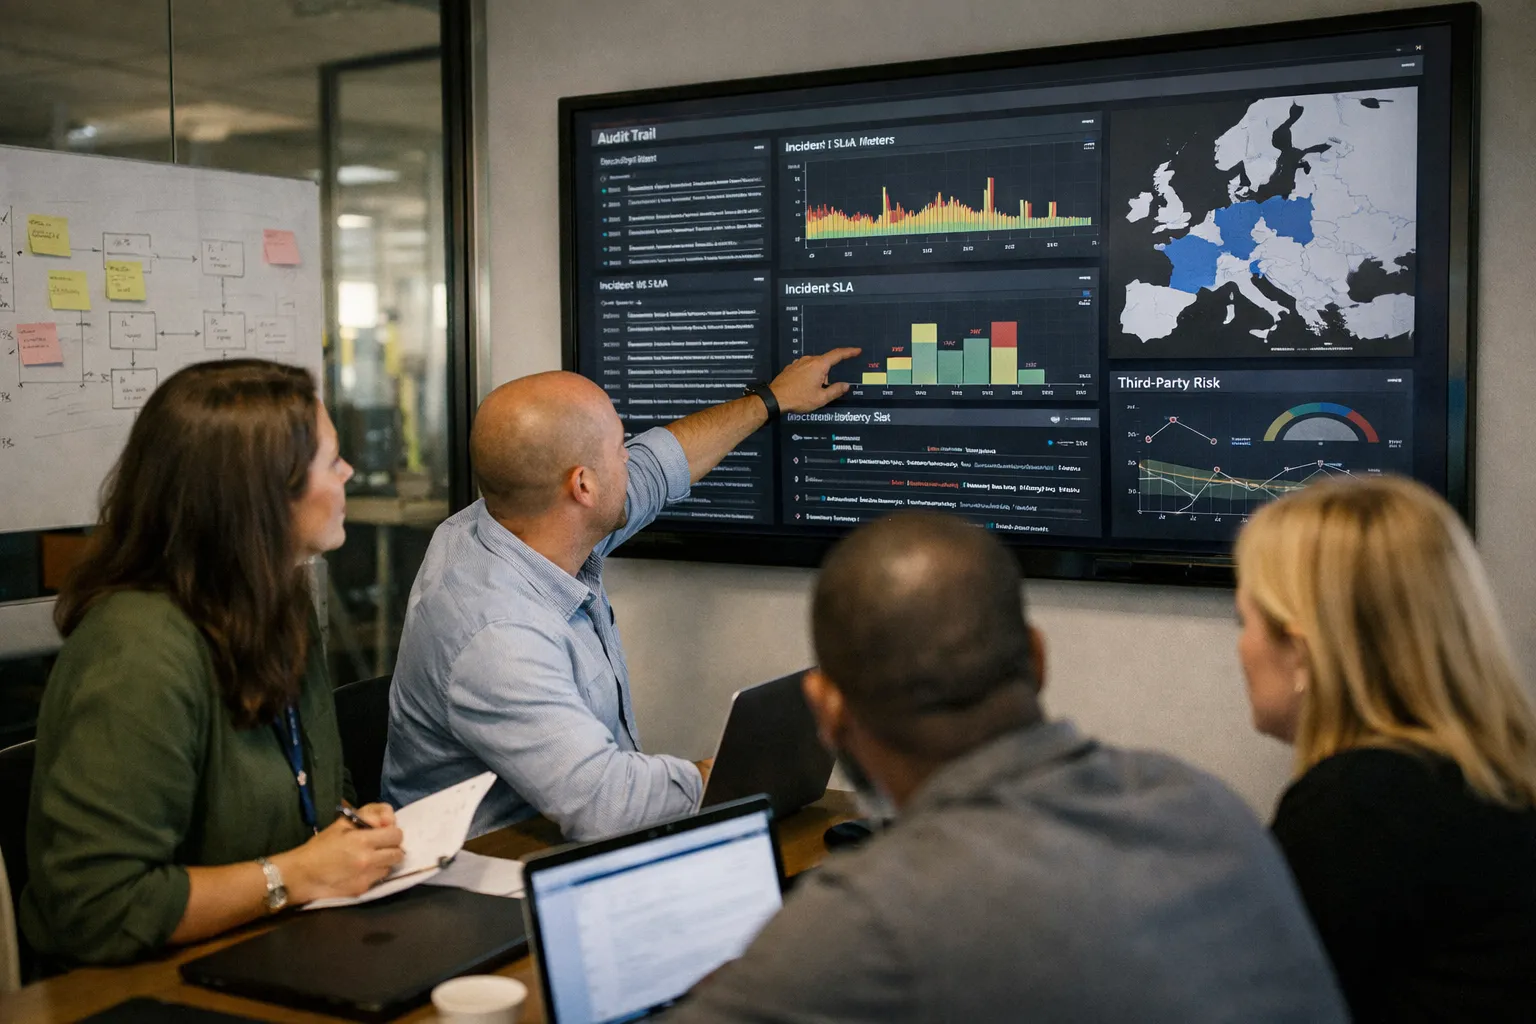
Who, what, when, where, why: As of August 2026, enforcement of the EU’s NIS2 directive (transposition deadline October 17, 2024) and the Digital Operational Resilience Act (DORA, in force for financial entities since January 17, 2025) has moved from policy to operational pressure for enterprise IT across Europe and for international vendors serving EU-regulated customers. Regulators’ emphasis on mandatory notification timelines, evidence-based audits and third‑party oversight means enterprise software vendors and buyers now must bake compliance features into products, integrations and delivery models rather than add them later.
Context: Why enforcement matters now
Both NIS2 and DORA broadened the footprint of regulatory obligations and tightened expectations for incident reporting, governance and ICT third‑party risk. The transposition deadlines passed in 2024 and DORA’s date in early 2025 have given national competent authorities and financial supervisors time to move into active supervision by 2026. That shift is meaningful: companies can no longer rely on one-off attestations during procurement—regulators expect operational evidence, repeatable controls and demonstrable vendor oversight.
What’s changed in 2026 — concrete trends
- Compliance-by-design is the default: Major enterprise platforms now include immutable audit trails, standardized telemetry export (OpenTelemetry-compatible formats), and built-in incident export in STIX/TAXII or machine-readable formats to speed regulator reporting and forensic analysis.
- Supply-chain artifacts are standard product outputs: Vendors increasingly publish Software Bill of Materials (SBOMs) and integrate Software Composition Analysis (SCA) into CI/CD pipelines as part of standard subscriptions for regulated customers.
- Contractual and API-based attestations: “Regulatory APIs” that return machine-readable attestations about service status, patch levels, and third‑party subcontractors are appearing in enterprise SLAs and procurement templates.
- Integrated third‑party risk tooling: Platforms now ship with connectors to common GRC tools (e.g., ServiceNow GRC, Archer), or provide embedded vendor risk workflows, making evidence collection repeatable and auditable for DORA’s ICT third‑party rules.
- Managed observability and runbooks: For customers without big security teams, vendors offer managed SOC/SIEM options with playbooks aligned to regulatory reporting windows and documented escalation paths.
Specific vendor and market examples
Enterprise vendors across categories have released compliance-focused capabilities. Examples in the market include:
- ITSM/GRC platforms: Several major ITSM vendors now publish packaged integrations and runbooks to automate NIS2/DORA incident submission fields and retention controls. Customers report shorter audit cycles when vendors supply pre-built export templates.
- Observability and SIEM: Observability platforms and SIEM providers have extended retention, immutable logging options and certified connectors for GRC and regulatory reporting, reducing bespoke engineering in large deployments.
- Cloud and PaaS providers: Cloud vendors have expanded compliance documentation, regional data controls and contractual attestations to address both transposition differences among EU member states and DORA requirements for financial entities.
Impact on implementation, scalability and ROI — updated guidance
The economics and timelines touted in 2024 have crystallized into predictable outcomes by mid‑2026:
- Higher initial license and deployment costs, but lower audit and legal spend: Buyers report paying more up front for solutions with embedded compliance features and attestations, yet savings appear in reduced consultancy engagements, fewer remediation cycles and faster regulatory sign‑offs.
- Fewer bespoke integrations, more contract obligations: Certified connectors reduce technical integration time, but procurement now negotiates SLAs, capacity guarantees and data residency clauses that materially affect TCO.
- Scalability and retention matter more: Regulators’ expectations for evidence retention and forensic ability mean platforms must guarantee longer log retention, tamper-evidence and search performance. Procurement must tie these needs to penalties and runbook obligations in contracts.
What CIOs and procurement teams should do now (practical, dated checks)
Updated checklist for August 2026:
- Map obligations to evidence: Translate NIS2/DORA clauses into the exact data elements you must produce (timestamps, immutable logs, chain-of-custody artifacts) and include those fields in RFP scoring.
- Insist on machine-readable incident exports: Require vendors to provide incident export in STIX/TAXII or a documented JSON schema that can be consumed by your GRC and SIEM tools.
- Require SBOMs and SCA outputs: For any critical component, demand a current SBOM and proof of SCA scanning integrated into CI/CD pipelines; include remediation timelines for critical vulnerabilities in contracts.
- Test surge scenarios: Run performance tests simulating concurrent incident filings and telemetry spikes; require capacity guarantees and retention SLAs tied to measurable KPIs.
- Embed audit and attestation clauses: Specify frequency and scope for SOC 2/ISO 27001 updates, enable auditing rights, and require a documented vendor incident playbook aligned to regulator timelines.
Regulatory nuance to watch
Not all EU member states have identical enforcement practices—national competent authorities interpret NIS2 transposition differently. Similarly, DORA supervision for third-party critical ICT service providers is phasing in and focuses heavily on contractual clarity and concentration risk (i.e., systemic dependency on a few providers). Procurement and legal teams must account for both pan‑EU obligations and local supervisory expectations when negotiating with vendors.
What vendors should prioritize now
- Deliver exportable, tamper-evident audit trails and standardized incident payloads.
- Publish SBOMs, SCA results and CI/CD attestations as standard deliverables for regulated tiers.
- Provide certified connectors to leading GRC and SIEM ecosystems and document reference deployments.
- Offer managed incident orchestration aligned to regulator timelines, with transparent runbooks and escalation metrics.
Impact and outlook
By August 2026 the market has moved: compliance is now a product and procurement differentiator. Buyers that insist on machine-readable evidence, SBOMs and capacity SLAs reduce regulatory risk and shorten audit timelines. Vendors that treat those features as core product capabilities—not professional services add-ons—gain competitive advantage with regulated buyers. Expect continued standardisation (machine-readable incident schemas, SBOM norms) and deeper integration between vendors, GRC platforms and national supervision workflows through the rest of 2026 and into 2027.
Frequently asked questions
How do I prove compliance quickly to a regulator?
Prepare machine-readable evidence: immutable logs, incident exports in STIX/TAXII or a documented JSON schema, SBOMs and SCA output. Ensure retention policies and access controls are in place and evidence is linked to an auditable chain-of-custody. These are the artefacts regulators will ask for first.
Should we require an SBOM from every vendor?
For critical systems and any ICT supplier considered important under DORA or NIS2, yes. SBOMs speed forensic analysis, clarify transitive dependencies and are now routine deliverables for regulated customers. Include remediation timelines for critical findings in contracts.
What contractual clauses matter most today?
Prioritise data retention and access, incident reporting format and timelines, capacity/availability SLAs, right-to-audit, and explicit third‑party subcontractor disclosure and attestations. Tie these to clear KPIs and remedies.
Is managed SOC a viable option for smaller regulated organisations?
Yes. Many vendors now offer managed observability and incident orchestration services with pre-aligned runbooks for NIS2/DORA timelines. These reduce operational overhead but verify contractual SLAs and evidence export capabilities before committing.