Introduction — What you'll learn and who this is for
This guide updates the 2026 playbook for data contracts in enterprise event-driven architectures (EDAs) and brings it to August 2026. It is written for integration architects, platform engineers, implementation leads and product owners who must keep event ecosystems reliable, auditable and scalable while preserving developer velocity.
Read this if you need a practical, phased approach to: choose schema formats and registry patterns, codify compatibility and policy-as-code, automate contract tests and CI/CD gates, observe adoption and business impact, and run a realistic pilot with measurable ROI. The advice reflects how registries, policy engines and observability tools stabilized across cloud vendors and open-source projects through mid‑2026, and translates that stabilization into operational patterns you can adopt immediately.
Prerequisites and context — what's new in Aug 2026
Since the spring of 2026 the discipline around data contracts moved from a best practice to a platform-level requirement for many enterprises. Key shifts to account for:
- Runtime enforcement is mainstream: Major managed event platforms and several service meshes now support schema-aware ingress/egress validation and transformations. That reduces reliance on consumer-side checks alone.
- Data catalogs and lineage tie contracts to business context: Organizations increasingly link schema registries to data catalogs (business glossary + lineage) so a schema change shows impacted products and SLAs in one view.
- Policy-as-code expanded beyond CI: Teams are encoding PII flags, residency and retention requirements in policy engines (Open Policy Agent remains common) and running those policies both at publish-time and in runtime gateways.
- Tooling ecosystem consolidated: AsyncAPI and CloudEvents conventions are widely used to describe semantics and event metadata; Confluent, Apicurio and cloud-managed registries (AWS, Azure, GCP variants) are default choices depending on platform strategy.
- AI-assisted review and migration tooling: In 2026, several vendors and open-source projects offer AI to surface risky schema changes, recommended migrations and probable consumer impact—useful as advisory input but not a substitute for domain review.
Before you begin, have:
- A prioritized list of business domains and event topics (billing, orders, inventory, customer lifecycle) with owners and a rough impact score (revenue, latency-sensitive, compliance).
- Access to or plan for a registry that supports versioning, access control and audit logging (Confluent Schema Registry, Apicurio Registry, cloud-managed registries, or a well-maintained open-source alternative).
- A cross-functional pilot team: producer owners, consumer representatives, platform engineers, security/compliance, product stakeholders, and a measurable set of KPIs to prove value.
Step 1 — Assess readiness and pick a pilot
- Inventory event flows. Export topics, sample payloads, producers and consumers. If tooling is limited, sample by traffic and business impact (pick the top 5–10 topics by volume or revenue exposure). Example: choose "orders-created" and "billing-invoice" if those feed downstream billing, analytics and CRM.
- Map stakeholders and risk. Identify owning teams, SLAs, compliance boundaries (PII/residency) and downstream dependencies. Record who can approve breaking changes and who must be notified.
- Define measurable success metrics. Agree on KPIs such as ingress validation pass rate, incidents caused by schema mismatch (target: reduce by X% baseline), mean onboarding time for a new consumer, and percent of consumers on the latest supported schema within 90 days (a practical baseline target is 75–90%).
Why it matters: a scoped pilot limits blast radius and produces measurable outcomes you can present to leadership and compliance.
Step 2 — Choose schema formats, contract-as-code and registry strategy
Format choice remains pragmatic and hybrid. Updated guidance for 2026:
- Schema formats: Use Avro or Protobuf for internal, high-throughput, typed systems. Use JSON Schema for partner-facing or analytics topics that benefit from human-readability. Publish AsyncAPI alongside schemas to document delivery semantics (ordering, retries, idempotency).
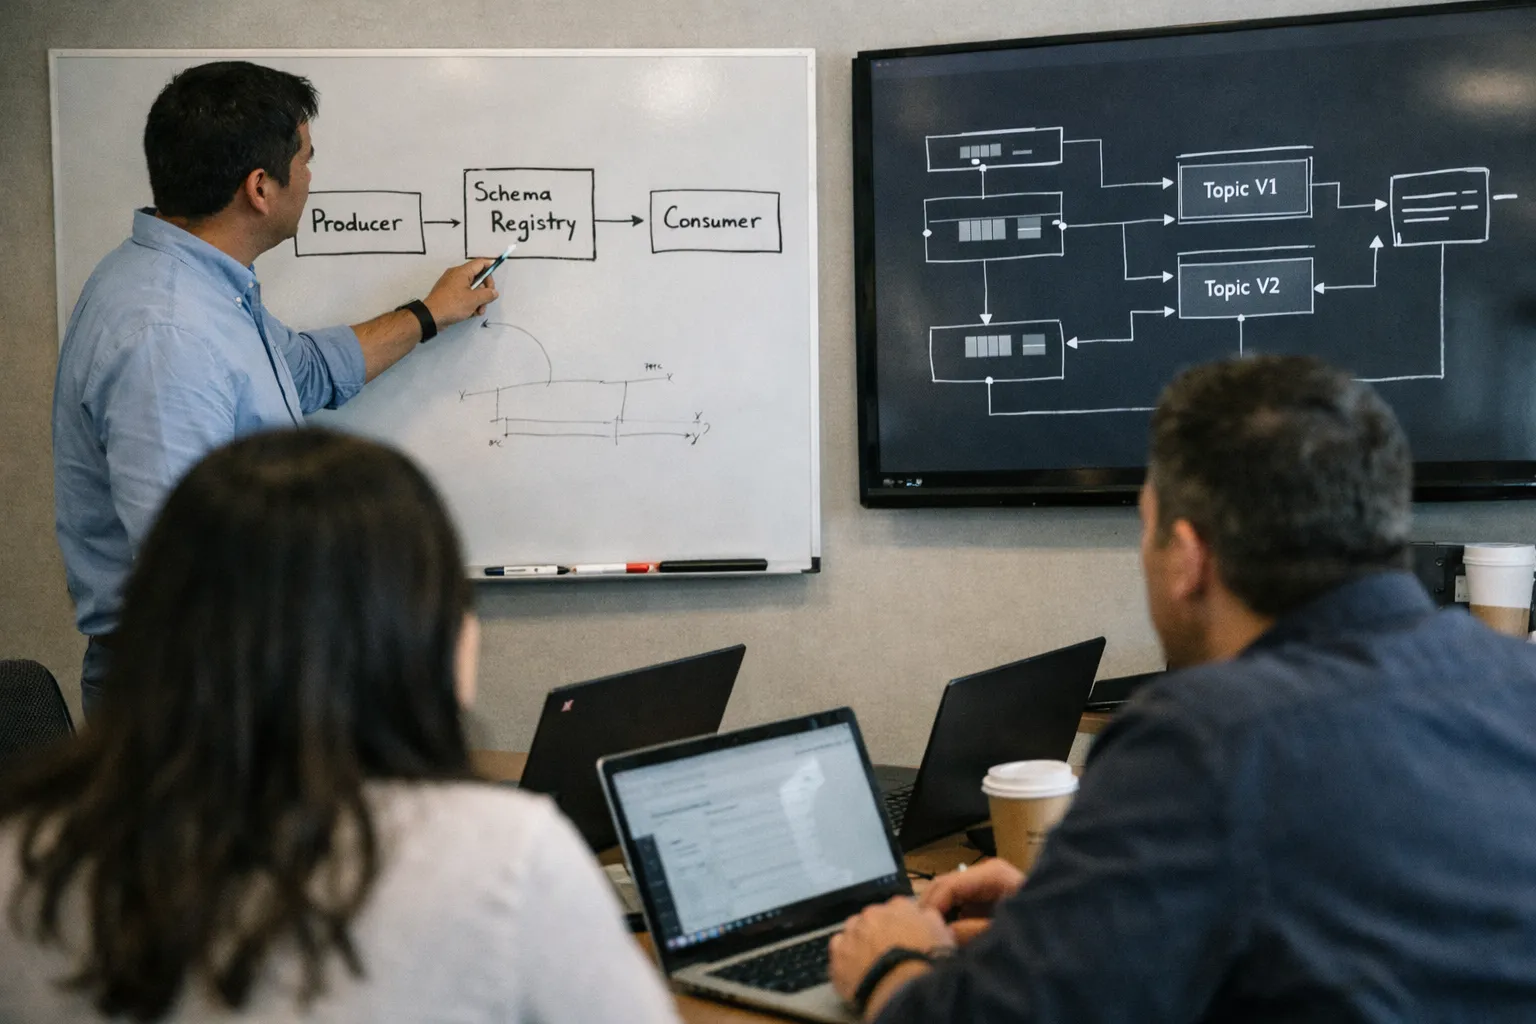
- Registry strategy: A single source-of-truth registry per platform remains best practice. Use built-in cloud registries when your workloads are primarily in one cloud; use Confluent/Apicurio for cross-cloud or hybrid environments. Ensure registry choice supports RBAC, audit logs and REST + CLI access for automation.
- Contract-as-code: Store schemas and AsyncAPI docs in a repo with PR reviews, signed releases and CI checks. Keep metadata (owners, deprecation windows, PII flags) in the registry and mirrored in the repo to avoid drift.
Why: registries and contract-as-code together enable discovery, automated validation, and an audit trail needed for audits and post-incident analysis.
Step 3 — Define compatibility, semantics and policy-as-code
- Pick a compatibility model explicitly. For broad consumer bases, mandate backward compatibility for producers. For tightly coupled teams, consider forward or full compatibility if you can coordinate release windows.
- Document semantics and lifecycle in the registry. Each field should have a description, units, PII flag, and deprecation timeline. Require example payloads and a "primary business use" tag—for example, "reconciliation", "fraud-detection".
- Encode policy-as-code. Use Open Policy Agent (OPA) or your platform's policy engine to enforce compatibility rules, residency flags, and PII constraints. Run these policies in CI and in the publish-time gateway so violations are prevented before publication and at runtime.
Why: policy-as-code automates guardrails and reduces manual friction while keeping an auditable change trail.
Step 4 — Governance, ownership and review workflow
- Contract owners: Assign a single owner per contract recorded in the registry; the owner is accountable for publishing, documentation and consumer migrations.
- Lightweight review with consumer representation: Use PRs for schema changes and require consumer approvers when changes affect required fields or semantics. Time-box reviews (48–72 hours) to avoid blocking velocity.
- Auditability and reporting: Ensure the registry stores who changed what and why. Produce quarterly summaries for compliance and business stakeholders that map contract changes to incidents and adoption metrics.
Why: maintain speed with control—overcentralization stalls teams, but under-governance creates hidden technical debt.
Step 5 — Automation: codegen, contract tests and CI/CD gates
- Code generation: Generate SDKs/DTOs for major languages from schemas and publish them to language-specific package registries. This reduces parsing errors and speeds consumer onboarding.
- Contract testing: Run provider-driven and consumer-driven contract tests. Integrate tests with your registry to fetch the active schema and execute as part of CI.
- CI/CD pipeline gates: Block merges that fail compatibility checks, policy-as-code rules or contract tests. Provide clear failure messages and remediation guidance so teams can fix quickly.
- Pre-production verification: Use shadow traffic, schema-aware replay tools and staging environments with ingress validation to validate consumer behavior before global rollout.
Why: automation scales governance and makes adherence the default, not a chore.
Step 6 — Rollout and migration patterns (Aug 2026 best practices)
- Additive-first changes. Prefer optional fields and clear examples. Publish release notes and AsyncAPI updates with each schema version.
- Platform-level transformations: For heterogeneous consumer ecosystems, use platform transformation adapters (registry-driven converters) to limit the need for dual-write. Where conversion isn't practical, use dual-write and feature flags.
- Deprecation and adoption tracking: Publish deprecation windows in the registry and automate notifications when consumers lag. Aim for at least 75% adoption within 90 days for typical internal topics; record exceptions for long-tail systems.
Why: phased rollouts and registry-led transformations reduce risk without requiring lengthy coordination.
Step 7 — Observability: validation, tracing and adoption metrics
- Ingress validation and quarantine: Validate incoming events at platform ingress and quarantine or route invalid events to a dead-letter inspection pipeline instead of silently dropping them.
- Trace context and end-to-end observability: Propagate trace and business-context (CloudEvents attributes and OpenTelemetry spans) so you can trace schema validation failures back to affected transactions.
- Adoption and operational metrics: Track validation error rate, schema adoption curves, consumer failures attributable to mismatches, and MTTR for contract-related incidents. Surface these on SLI/SLO dashboards (for example: target 1% ingress validation errors; MTTR under one business day for schema-related incidents).
Why: observability links contract discipline to business outcomes and shortens time to remediate issues.
Step 8 — Measuring ROI and business impact
Translate technical improvements into business metrics and show clear returns:
- Reduction in integration incidents attributable to contract issues (compare pre‑pilot and post‑pilot counts).
- Onboarding time for new consumers—measure from the request to production consumption; aim to reduce this by 30–50% using codegen and published SDKs.
- Percentage of production events validated at ingress and reductions in emergency hotfixes or rollbacks.
- Developer time saved (estimate hours per week) and operational cost savings from fewer incidents.
Why: demonstrating ROI—quarterly—is the strongest way to sustain investment in registries and platform features.
Common mistakes and how to avoid them
- Overcentralization: Avoid heavy gatekeepers. Automate checks and require consumer representation in reviews.
- Poor semantics: Schemas without field descriptions, units or PII flags force ad hoc consumer behavior. Enforce metadata requirements in the registry.
- No runtime enforcement: Publishing contracts without runtime validation makes contracts aspirational. Enforce policies at publish-time and at ingress/egress.
- Ignoring observability: Contracts without metrics and tracing hide failures. Instrument adoption and validation metrics from day one.
- Overreliance on AI: Use AI-assisted suggestions for migration risk, but retain human domain review—AI is advisory, not authoritative.
Pro tips — advanced patterns for Aug 2026
- Link registry to data catalog and lineage tools: When a schema change is proposed, show impacted downstream products, SLOs and owners in one UI.
- Use OPA at both CI and runtime: Encode residency, encryption and PII handling policies once and evaluate them where they matter most—before publish and at the gateway.
- Rotate "contract stewards": Rotate a cross-functional steward role quarterly to spread knowledge and avoid single‑person bottlenecks.
- Adopt schema-aware service meshes or brokers: Where possible, offload simple transformations and validation to platform components to reduce application complexity.
Realistic timeline for an enterprise pilot (Aug 2026)
- Weeks 1–3: Inventory, stakeholder alignment, select pilot topics and define success metrics.
- Weeks 4–8: Configure registry, add AsyncAPI docs, implement contract-as-code repo, wire CI validations and produce SDKs for pilot teams.
- Weeks 9–16: Execute contract tests, run shadow traffic and staged rollouts, add ingress validation, and create observability dashboards linked to business KPIs.
- Weeks 17–24: Expand to adjacent domains, refine governance and policy-as-code rules, compile ROI report for leadership and plan enterprise scaling (automation, transformations, and training).
Why this matters now
By August 2026, enterprises run event ecosystems that cross hybrid clouds, regulated geographies and third-party partners. Without explicit contracts—schema + semantics + operational controls—teams trade short-term speed for long-term fragility. With registries, policy-as-code, runtime validation and integrated observability, data contracts become an enabler of predictable velocity and auditability, not a bottleneck.
Common questions
How do data contracts differ from API contracts?
API contracts (REST/gRPC) define synchronous request/response interactions; data contracts govern asynchronous events and must include schema, semantic documentation and delivery expectations (ordering, idempotency, retention). Event contracts also need explicit lifecycle and ownership metadata and often require runtime validation at ingress.
Should I use Avro/Protobuf or JSON Schema?
Choose based on trade-offs: Avro and Protobuf provide compact binary formats and strong typing for high-throughput internal streams. JSON Schema is human-readable and simpler for ad hoc consumers or external partners. Many teams use both: binary formats internally and JSON for partner or analyst-facing streams—publish AsyncAPI to document cross-format semantics.
How do I enforce contracts without slowing teams down?
Automate enforcement via CI/CD gates, registry policies and runtime validation. Provide SDKs and codegen so consumers and producers have typed models. Use lightweight human review only when automated checks flag semantic or required-field changes.
Can data contracts help with compliance and privacy?
Yes. Record PII flags, masking and residency metadata in contracts and enforce them with policy-as-code. Run those policies in CI and at runtime gateways so invalid flows are blocked and you retain auditable evidence for audits.
When should I trust AI recommendations for schema changes?
AI tools are helpful to flag risky changes and suggest migration paths, but always combine AI output with human domain review—particularly for fields that affect compliance, billing or security. Treat AI as advisory, then require owner sign-off recorded in the registry.
Implementation note: This guide condenses operational patterns proven in enterprise pilots. Every organization has unique constraints—consult your platform and compliance teams when defining contract policies and retention rules.
Start small, instrument every change, and iterate governance to balance control and velocity. With concrete contracts, automated enforcement and integrated observability, event-driven systems can deliver predictable, auditable integration at scale.